Have any questions?
Call (276) 601-3208
RiverTrail Technology
|
Call (276) 601-3208
It usually happens slowly. You buy a basic antivirus program when you first open your doors. A couple of years later, someone sells you an email filter. Then maybe you pick up a separate firewall box because a compliance form asked for it.
Before you know it, you're running three or four different security applications across your office terminals that have never spoken a word to each other (and couldn't if they tried).
When team members bypass IT security guidelines, it is almost never out of malice or bad intentions. In nearly every case, employees are simply trying to get their daily work done without running headfirst into digital brick walls that slow them down.
Understanding security friction is the first step toward fixing it.
Banning AI tools across your entire organization rarely works. When employees face flooded inboxes, tight deadlines, or long documents that need summarizing, they will turn to whatever software helps them get through the workday.
Locking down your network to block these platforms usually just pushes the behavior out of sight. The real solution is establishing practical guardrails so your team gets the productivity benefits while your confidential data stays inside your organization.
Business owners often joke about their technology management to blow off steam. Password strategies, outdated hardware, and skipped system updates frequently turn into running jokes around the office. Laughing about these issues feels natural because technology can be frustrating, complex, and expensive.
The bad news is that cybercriminals do not share your sense of humor. Treating network security like a joke leaves your operations exposed to real financial and operational damage.
Chances are, your team is regularly saving PDFs, client spreadsheets, and presentation decks directly to their local Documents folder or Desktop. Storing business files on physical laptop hard drives has been standard practice for decades, but it exposes your organization to hidden operational costs and unnecessary risk.
Allowing corporate data to live on physical endpoints creates security blind spots and compliance headaches. Here is why transitioning your team to a centralized cloud workspace is one of the most effective moves you can make for your business this year.
Imagine your business has just suffered a data leak. Your IT staff are isolating the breach, patching the vulnerability, and restoring your systems from backups. While this looks like a victory, it’s important that you consider the other ramifications that come from such an incident—including the damage it can do to your company’s reputation.
If your technology is the foundation of your business’ daily operations, it shouldn’t be treated as an afterthought or a chore. Unfortunately, it often is. So, while shortcuts might save a few minutes today, they routinely compromise your security and stability. Today, I want to go through five potentially critical mistakes that put your operations at serious risk.
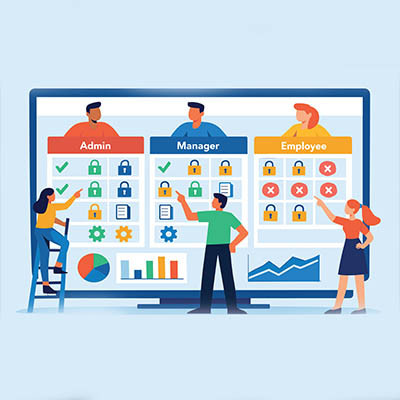
When you first started your business, chances are you were the “keeper of the keys,” so to speak. You registered the domain, set up the billing accounts, and held the master login for every piece of critical software your business uses. But as your business has grown, how useful has that model been? Has it turned into an operational bottleneck where your attention is pulled away from your important founder work?
As small and medium-sized businesses expand their remote work capabilities, the technical systems that once supported them must evolve. For many years, virtual private networks served as the standard tool to connect remote employees to physical office servers. However, relying on a legacy VPN is no longer a sustainable long-term strategy for growing organizations. Approximately 88 percent of companies report being concerned that traditional VPNs jeopardize their overall security posture.
When your business expands, a legacy VPN will eventually fail to meet your operational, compliance, and security requirements. Understanding the technical limitations of this older framework and preparing for modern upgrades are critical steps for every growing business.
We are right in the thick of summer vacation season. Over the next few weeks, your office is likely going to look a little sparse. Managers are taking well-deserved time off, key decision-makers are heading out of town, and daily operations are being left in the hands of smaller, temporary skeleton crews.
It’s a great time for your team to recharge, but it is also a prime operational window for cybercriminals. Scammers don't take summer vacations. In fact, they look forward to this time of year because they know the normal checks and balances of a local office are temporarily compromised.
For all that pop culture has done to cultivate the slick, cool loner persona of a hacker, it bears little relation to reality. In many cases, data theft is extremely corporatized. Frankly, it can be boring.
Unfortunately, this makes it no less dangerous. These cybercriminals are quiet and meticulous in their work, invisibly pulling your data out over the course of weeks or months. The worst part: if you don’t know what to look for, you could completely miss the subtle warning signs.
Delaying technology upgrades until hardware or software breaks completely is a common practice for many small business owners. This approach feels financially conservative, but it actually creates an unhedged operational liability. Choosing to hold off on necessary infrastructure improvements creates predictable risks that eventually disrupt daily operations and drain financial resources.
The average small business relies on dozens of different web platforms to handle daily operations, including billing, customer tracking, and team communication. For staff, this digital growth creates severe password fatigue. When employees are forced to remember dozens of complex logins, it leads to a constant loop of locked accounts, broken workflows, and lost productivity that stalls the business day.
Small businesses regularly invest thousands of dollars into sophisticated digital defenses—centrally managed firewalls, enterprise email filters, and endpoint software protection—to keep hackers out of their networks. The problem is, many of those same organizations leave their physical network hardware completely exposed. It is common to find main network switches sitting on open shelves in shared spaces like copy rooms, or located in server closets that are left completely unlocked.
Every technology provider has a list of core values on their website. They use words like efficiency, innovation, and speed. And while we use these outcomes as much as anyone, we want to be completely candid about the ultimate boundary line in modern IT. Today, there’s a constant tug-of-war between security and convenience.
Computer updates frequently appear on screen during the workday. For most of your employees, the immediate choice is to click the option to delay the update because they have pressing responsibilities. However, delaying these updates creates a patch gap, which is a significant security vulnerability for a small business.
Employees are the largest vulnerability in any business network. A single mistake by a staff member can bypass established security infrastructure. Cybersecurity is an organizational culture requirement rather than a purely technical one. Protecting a business requires educating the staff on how to identify and avoid digital traps.
Cybersecurity training fails when it prioritizes compliance over actual office workflows. Most programs provide generic information that does not help a non-technical person manage their daily tasks. When training feels like an interruption rather than a tool, employees will naturally ignore the content to focus on their primary job responsibilities.
Checking a box on an insurance application is no longer enough to protect your business. Insurance carriers have faced record payouts and are now fighting back by mandating strict technical standards.
As a result, if you cannot prove you have specific protections in place, you may find your premiums skyrocketing; or worse, your claim denied after an incident occurs.
Bring Your Own Device, or BYOD, used to be thought of as a win-win. Employees could use phones they were used to, while businesses could avoid spending thousands of dollars on new hardware. While BYOD is convenient and solves multiple problems for your business, it’s crucial that you also remember the inconvenient truth: that BYOD is insecure unless you take action to secure it.
Learn more about what RiverTrail Technology can do for your business.
RiverTrail Technology
103 North Monroe St
Galax, Virginia 24333
You can return any item purchased on our website within 30 days of the purchase date.